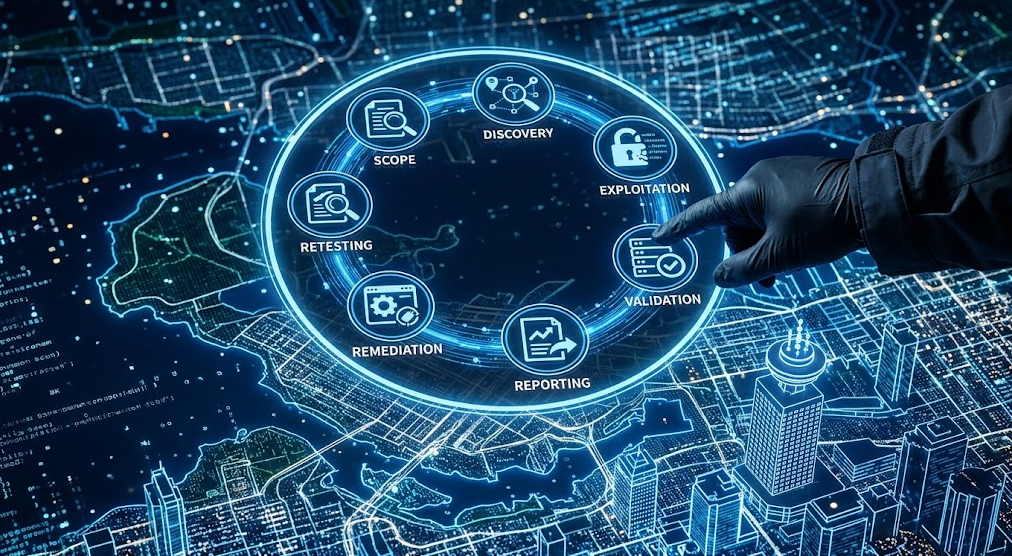
Professional penetration testing is a structured security assessment rather than an unrestricted attempt to break into a system. The process normally begins with scope definition and planning, continues through reconnaissance and controlled exploitation, and ends with reporting, remediation guidance, and retesting.
Understanding this lifecycle helps both technical and non-technical stakeholders know what to expect from penetration testing services Vancouver. It also explains why preparation and reporting are just as important as the technical testing itself.
1. Scope and Planning Come First
A professional assessment starts by defining boundaries.
Before testing begins, the organization and testing team should establish which systems are authorized for assessment and which are excluded. This can include domains, IP addresses, applications, APIs, cloud resources, authentication environments, or internal network segments.
Planning may also address:
- Testing dates and working hours
- Emergency contacts
- Permitted testing techniques
- Systems requiring special care
- Authentication credentials
- Testing limitations
- Rules for handling discovered information
Clear scope prevents misunderstandings and helps keep testing aligned with business requirements.
2. Reconnaissance Builds the Technical Picture
Reconnaissance involves collecting information about the approved target environment.
For an external assessment, testers may examine publicly available information and identify exposed services. During an authenticated application assessment, they may map application functionality, user roles, endpoints, and data flows.
The purpose is to understand what is actually exposed.
This phase can reveal unexpected assets such as forgotten subdomains, legacy applications, exposed administrative interfaces, or API endpoints that deserve further investigation.
3. Vulnerability Discovery Examines Potential Weaknesses
Once the environment is mapped, testers look for vulnerabilities and security-control weaknesses.
This can involve both automated tools and manual techniques.
Potential findings may include:
- Weak authentication mechanisms
- Broken access controls
- Injection vulnerabilities
- Insecure configurations
- Exposed services
- Session-management weaknesses
- API authorization problems
- Outdated or vulnerable components
Automated tools can increase coverage, but human analysis is necessary to understand context and determine whether an apparent issue has meaningful security consequences.
4. Controlled Exploitation Validates Risk
Finding a potential vulnerability does not automatically mean it can be meaningfully exploited.
Controlled exploitation is used to validate important findings without causing unnecessary damage.
For example, if an application appears to allow unauthorized access to another user’s record, a tester may safely demonstrate the access-control failure using designated test data. The purpose is to establish evidence, not to disrupt production systems.
This distinction is central to professional penetration testing.
The testing team should work within the agreed rules of engagement and avoid actions that could unnecessarily affect availability or data integrity.
5. Attack Paths Reveal Relationships Between Weaknesses
Individual findings can sometimes appear less serious when viewed separately.
Consider a hypothetical environment with three issues:
- A low-privilege account can access an administrative function.
- The administrative function exposes an internal identifier.
- That identifier can be used to reach sensitive information.
The combined path may be much more significant than any single observation.
Attack-path analysis helps organizations understand how weaknesses interact. This provides a more realistic picture of risk than simply sorting a spreadsheet by severity labels.
6. Validation Separates Evidence From Assumptions
Professional testing should distinguish confirmed findings from possibilities.
A scanner might report a suspected vulnerability. The tester then investigates whether the condition exists, whether exploitation is possible, and what access or information could actually be obtained.
Validation improves the quality of the final report because security teams receive evidence rather than an unfiltered list of potential problems.
7. Risk Analysis Adds Business Context
Technical severity alone does not always determine remediation priority.
Risk analysis can consider:
- Exploitability
- Asset importance
- Data sensitivity
- Required privileges
- Exposure level
- Business impact
- Existing compensating controls
A vulnerability on an isolated development server may require different treatment from the same vulnerability on a public-facing system containing sensitive customer information.
This context allows decision-makers to allocate remediation resources more intelligently.
8. Reporting Turns Testing Into an Action Plan
A strong report should explain what was found and what should happen next.
Useful reporting commonly includes:
- Executive-level summary
- Technical findings
- Affected systems
- Evidence
- Risk explanation
- Remediation recommendations
- Severity or prioritization
- Testing limitations
The executive section should help leadership understand the overall security picture without requiring deep technical knowledge.
Technical teams need enough evidence to reproduce or investigate the issue and implement an appropriate fix.
9. Remediation Addresses the Root Cause
Fixing the visible symptom is not always enough.
If several endpoints suffer from an authorization problem because access control is implemented inconsistently, fixing one endpoint may leave the underlying design issue intact.
Organizations should therefore ask:
Why did this weakness exist?
The answer may involve development practices, configuration management, identity architecture, deployment processes, or insufficient security testing.
Addressing the root cause can prevent similar weaknesses from appearing elsewhere.
10. Retesting Confirms the Fix
Retesting provides a final verification step.
After remediation, testers can revisit important findings and determine whether the original weakness has been resolved. In some cases, retesting may also identify whether the fix introduced a different problem.
This closes the loop between discovery and improvement.
Key Takeaway
A professional penetration test is a lifecycle: scope, reconnaissance, discovery, controlled exploitation, validation, risk analysis, reporting, remediation, and retesting. Each stage contributes to the reliability and usefulness of the final assessment.
Conclusion
The strongest penetration-testing engagements do more than uncover vulnerabilities. They provide evidence, context, and practical guidance that security and development teams can use to improve the environment.
Understanding the process also helps organizations prepare better, communicate expectations clearly, and turn assessment findings into measurable security improvements.
